
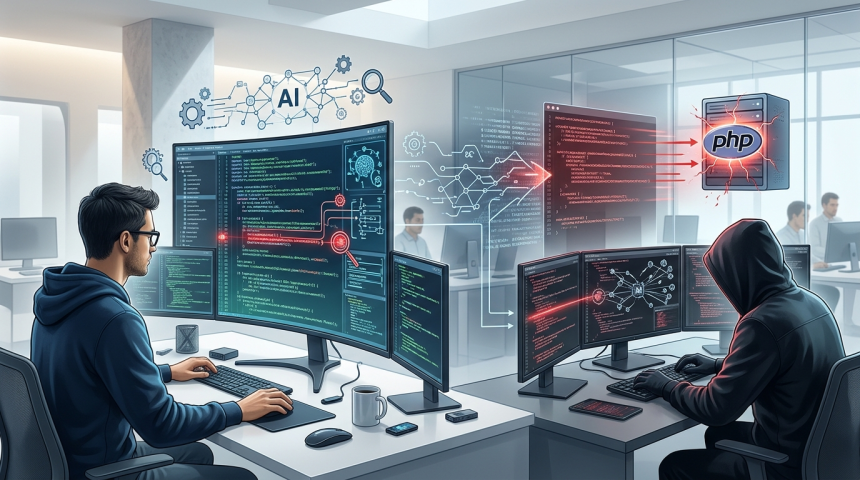
Security researchers used artificial intelligence tools to uncover years-old flaws in PHP, only for AI-assisted attacks to follow the discoveries. The sequence highlights a growing problem for web security: the same systems that help defenders inspect code can also help attackers move faster.
PHP is a scripting language used to build websites and online services. Its long history and wide use make its security important to companies, public agencies, developers, and website visitors.
Old Code Faces New Scrutiny
The vulnerabilities had remained hidden for years before researchers found them with AI support. That suggests automated tools can identify weaknesses that survived earlier reviews, testing, and routine maintenance.
Older software often contains code written under different security standards. Over time, new features, patches, and integrations can make that code harder to assess. AI tools can assist by reviewing large volumes of material and flagging unusual patterns for human investigation.
Security researchers used AI tools to help uncover years-old vulnerabilities in the PHP web scripting language. Then the AI-assisted attacks began.
The findings do not show that AI worked alone. Security research still requires people to confirm whether a suspected weakness can be exploited, judge its severity, and develop a safe repair.
Defensive Research Creates a Risk Window
Finding a flaw is only the first stage of the response. Software maintainers must prepare and test a patch. Website operators must then install it without disrupting their services.
Attackers may use that period to study public disclosures, compare patched and unpatched code, or search for exposed systems. AI can speed parts of that work by helping users read code, draft scripts, and adapt known attack methods.
The central issue is speed and access. Tools that lower the effort needed for defensive analysis may also reduce the effort required to build attacks. This gives organizations less time to act after a vulnerability becomes known.
The reported sequence points to several priorities:
- PHP maintainers need careful disclosure and patching processes.
- Website operators need accurate software inventories and rapid updates.
- Security teams need monitoring for attack patterns linked to newly reported flaws.
- Researchers need safeguards when using AI to test sensitive code.
Responsibility Remains With People
AI can strengthen code review, but it can also produce incorrect findings or unsafe suggestions. Human verification remains necessary before researchers publish a claim or organizations change production systems.
A balanced response should avoid treating AI as either a cure or the sole cause of the threat. Vulnerabilities existed before these tools found them. Attackers also used automation long before modern generative AI became widely available.
Still, AI may compress the time between discovery and exploitation. That shift could place smaller organizations at greater risk because they often lack dedicated security staff or automated patch systems.
PHP Users Face a Clear Test
For organizations running PHP services, the immediate lesson is practical. They should identify deployed versions, follow official security notices, apply supported updates, and review logs for suspicious activity. Unsupported software deserves special attention because fixes may not be available.
The episode also tests how software projects handle AI-assisted research. Clear reporting channels and coordinated release plans can give maintainers time to fix defects while reducing unnecessary exposure.
The broader outcome will depend on whether defenders can turn faster discovery into faster protection. If patching remains slow, AI-assisted research may expose gaps that attackers can exploit. If maintenance and monitoring improve, the same tools could help remove old weaknesses before they cause wider harm.